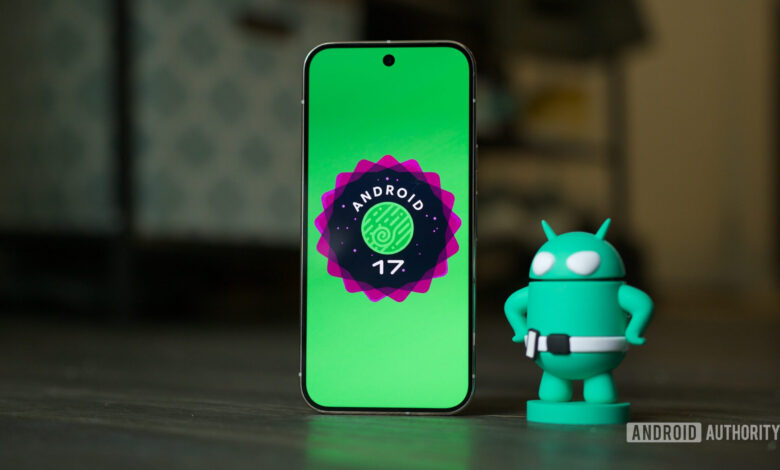
Android 17 Enhances Mobile Privacy with New Network Security Upgrades
Securing mobile hardware against evolving digital threats is a continuous effort, and Google is taking further steps to shield user data in Android 17. The upcoming version of the operating system introduces a series of low-level network security updates designed to protect personal data from eavesdropping, restrict unauthorized app behaviors, and neutralize rogue cellular transmitters.
Blocking Privacy Leaks with Encrypted Client Hello
One of the most notable additions in Android 17 is broad support for Encrypted Client Hello (ECH). While modern web traffic relies heavily on encryption to safeguard sensitive content, traditional domain lookups have long left a privacy loophole open. Even when visiting an encrypted website, the initial connection request—specifically the server name—was frequently transmitted in plain text. This allowed internet service providers, network administrators, or third-party observers to monitor which domains a user was attempting to reach.
ECH addresses this vulnerability by fully encrypting the server name during the initial connection setup. To prevent eavesdroppers from identifying unencrypted traffic patterns, the system sends randomized filler data when connecting to servers that do not yet support the protocol. By building native support into Android 17, Google becomes the first major mobile platform vendor to adopt ECH at scale, a move expected to encourage website administrators worldwide to implement the security standard.
Defending Against Fake Cell Towers and SMS Blasters
Android 17 also strengthens defenses against cellular-based threats, such as rogue cell towers often referred to as “stingrays” or “SMS blasters.” Attackers use these illegitimate transmitters to intercept mobile traffic or broadcast unsolicited spam and malicious links directly to nearby phones, frequently by forcing devices onto legacy, unencrypted 2G connections.
To counter these attacks, the updated OS gives mobile carriers the authority to enable automated defenses by default. Under this system, network operators can restrict vulnerable 2G connections and block fraudulent broadcasts automatically, protecting users without requiring them to navigate complex security settings.
Restricting Local Network Probing and Enforcing Certificate Transparency
In addition to cellular and internet-wide protections, Android 17 tightens controls over how applications interact with local networks. Previously, intrusive apps could silently scan a user’s home Wi-Fi network to identify connected devices, perform device fingerprinting, or search for unpatched security flaws in smart home hardware. Android 17 restricts this local network visibility, preventing unauthorized probing.
Furthermore, the OS now enforces Certificate Transparency by default. This protocol ensures that every connection established by the device relies on legitimate, publicly logged SSL certificates, significantly reducing the risk of man-in-the-middle attacks resulting from compromised or fraudulent security credentials.